Cybersecurity & POPIA
Security described in controls and evidence, not fear.
Security problems in small firms usually start with the basics: a reused password, an untested backup, a convincing e-mail. Adamant Tech puts the controls in place and shows the evidence, for small firms that hold client data and for larger organisations that need independent assurance. Senior-led, with no scare tactics and no claims that cannot be verified.
Small firms that hold client data
- Multi-factor authentication deployed and enforced
- E-mail security and anti-phishing
- Managed endpoint detection, under Essentials + Security
- Annual staff phishing exercise
- Incident register and a breach-response one-pager
- Staff security-awareness session, built around the firm’s own tools and policies
POPIA Compliance Starter
- Gap assessment
- Policy pack: privacy policy, data-handling procedures and consent wording
- Information Officer guidance
- Incident register and breach-response plan
- One staff training session
The starter takes about three to four weeks and is quoted as a fixed price after scoping. It is a practical compliance service and not legal advice.
Enterprise assurance
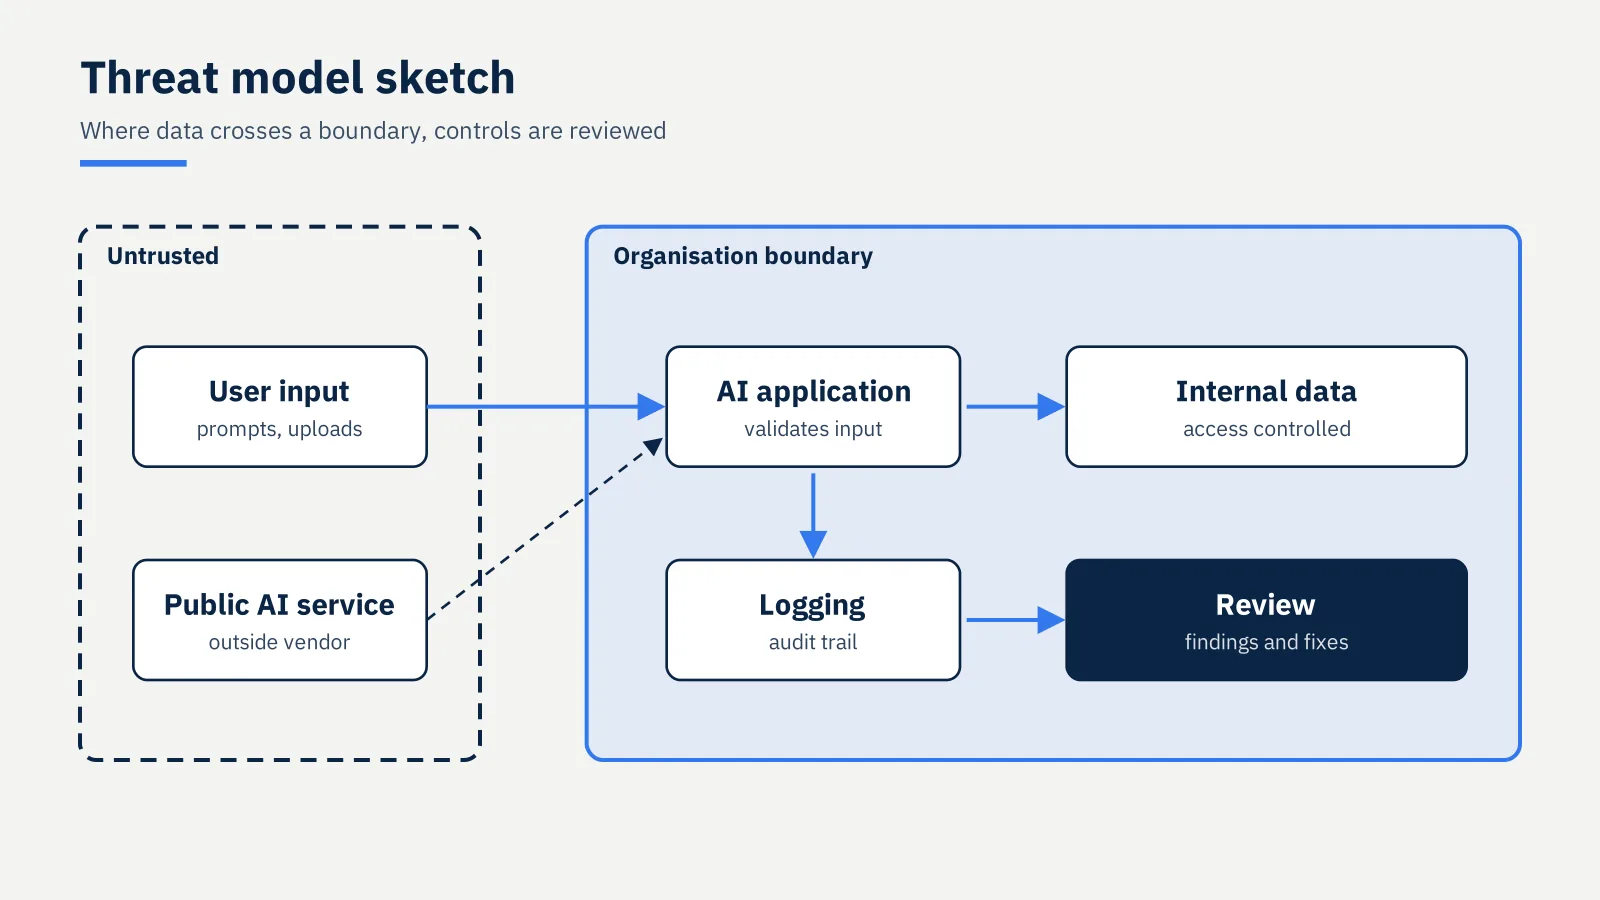
- AI security assessment: a threat model of the AI surface covering prompt injection, data leakage, vendors and supply chain, and access control, with a review of controls and a prioritised remediation register
- Security reviews of cloud and identity
- POPIA gap assessment
- Fractional security leadership
Enterprise work is quoted per engagement.
How it runs
Scope, assessment, findings in plain language, a prioritised plan, then optional follow-through.
Not included
Penetration testing, certification audits, representation before the Information Regulator, legal advice, investigation of crimes already committed, recovery of stolen funds or accounts, and incident response outside an agreed engagement.